Prompt Injection as a First-Class Threat: How to Model It Properly
1. Introduction Every major technology wave has its defining class of vulnerability. For web applications, it was SQL injection — a simple but devastating flaw caused by mixing untrusted data with executable instructions. Prompt injection is the modern equivalent for GenAI systems. In LLM-powered applications, the model treats natural language as both data and control […]
Threat Modeling AI Systems: Why STRIDE Alone Is Not Enough
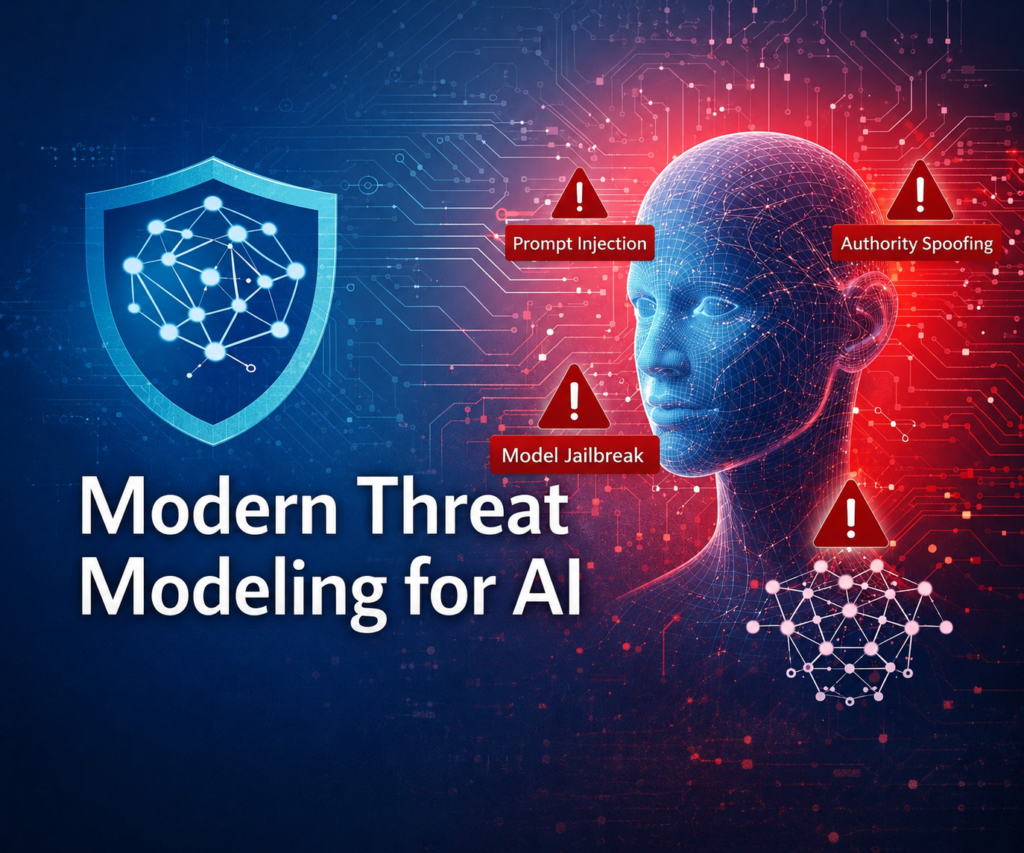
Threat Modeling AI Systems is reshaping how we think about security. STRIDE has been a reliable framework for decades, but it struggles to address the unique risks introduced by GenAI, LLMs, RAG pipelines, and agentic workflows. This article covers STRIDE’s gaps, emerging AI threat categories, and practical ways to modernize your threat modeling strategy. 1. […]
OWASP Top 10 Web Vulnerabilities: Are You Still Exposed?
Key Takeaways What Security Teams Should Know Immediately Broken access control remains the most critical vulnerability, allowing unauthorized users to access restricted areas, features, and sensitive data they shouldn’t see. The OWASP Top 10 reflects real-world attacks businesses face regularly—ignoring these vulnerabilities puts your data, customers, and reputation at serious risk. Weak authentication, missing encryption, […]
Internal vs. External Network Penetration Testing: Which Does Your Business Need?
As a business owner, you probably hear a lot about cybersecurity. But how do you know what your business actually needs? One important term you might have encountered is “penetration testing”—also called “pen testing.” In simple terms, it is like hiring a professional to safely break into your own systems to find weak spots before […]
iOS vs Android Security: Which Platform Has More Vulnerabilities in 2026?
Key Takeaways What Security Teams Should Know Immediately iOS has fewer vulnerabilities by design, but no platform is 100% immune to attacks or sophisticated phishing threats. Android faces higher vulnerability exposure due to fragmentation, delayed updates across devices, and flexibility in app installation sources. Security depends more on management than the platform itself—a well-managed Android […]
Mastering Sourcegraph for Bug Bounty: Advanced Code Dorking Techniques
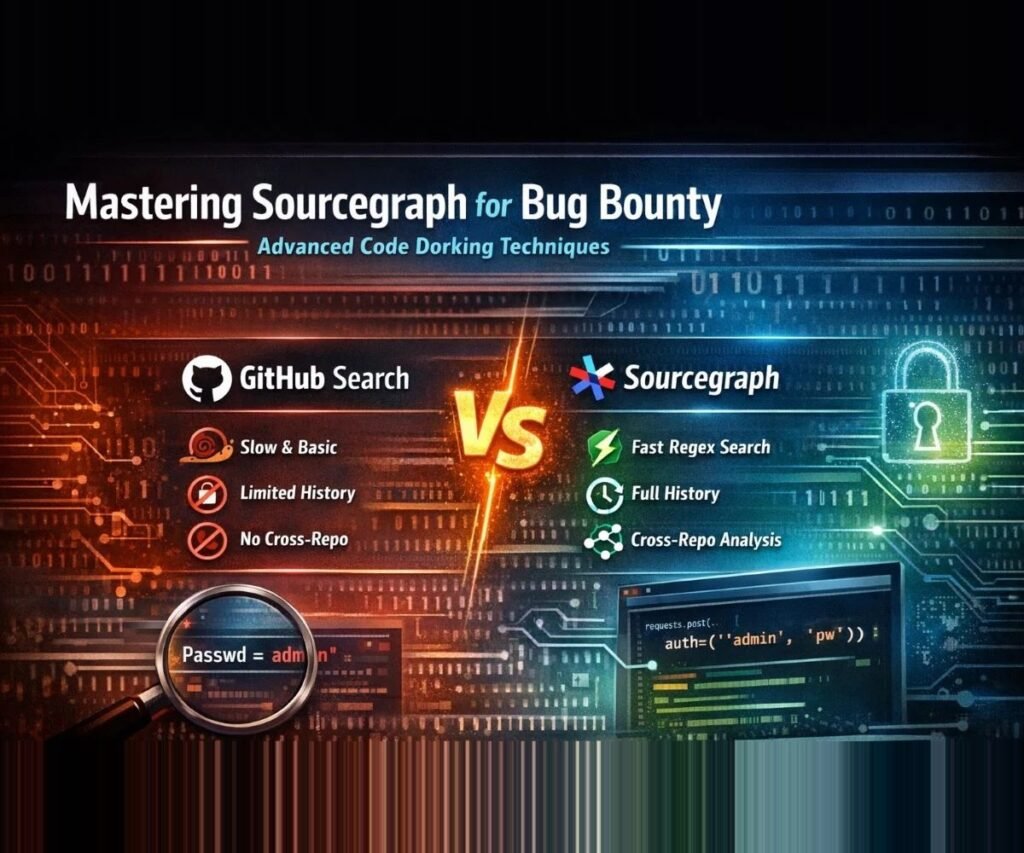
Key Takeaways What Security Researchers Should Know Immediately Sourcegraph outperforms GitHub search for security auditing, especially across large repositories and complex code patterns. Regex, structural search, and Boolean logic help bug bounty hunters uncover hidden vulnerabilities faster. Historical commit analysis is a major advantage, making it easier to find deleted secrets and legacy exposures. Targeted […]
How I’d Break Your LLM System: A Red Team Perspective on LLM Security Testing
A Red Team Perspective on LLM Security Testing Large Language Models (LLMs) are being rapidly integrated into enterprise systems — from customer support automation to internal knowledge assistants and workflow orchestration. But most organizations are assessing LLM security using traditional application security checklists. As a VAPT analyst, I approach it differently. I don’t ask: “Does […]
Axios Under Attack: What the 2026 NPM Supply Chain Breach Means for Your Security
Key Takeaways What Security Teams Should Know Immediately Axios was targeted via npm, turning a trusted package into a supply chain risk. The malicious package used staged dependency behavior to reduce suspicion and improve delivery. The attack path focused on post-install execution, making CI/CD and developer environments especially exposed. Primary impact includes credential and secret […]
DDoS Attacks Explained: How to Detect, Prevent & Respond
The internet faces many types of cyberattacks, yet Distributed Denial of Service (DDoS) attacks are among the most disruptive threats. These incidents have affected businesses, government agencies, online platforms, and even small websites. During these attacks, systems experience severe performance issues that can lead to complete service outages. Many people still ask a simple question: what is a DDoS […]
Local Storage vs Cookies: Securely Store Session Token
A system requires a method to maintain user sessions which becomes essential when users access a website through their login credentials. Without that functionality, people would need to authenticate themselves again after each page refresh. Browsers store authentication information using small data elements. The two most common storage methods are cookies and local storage. Developers often debate local storage vs cookies […]